Donate to support Ukraine's independence.
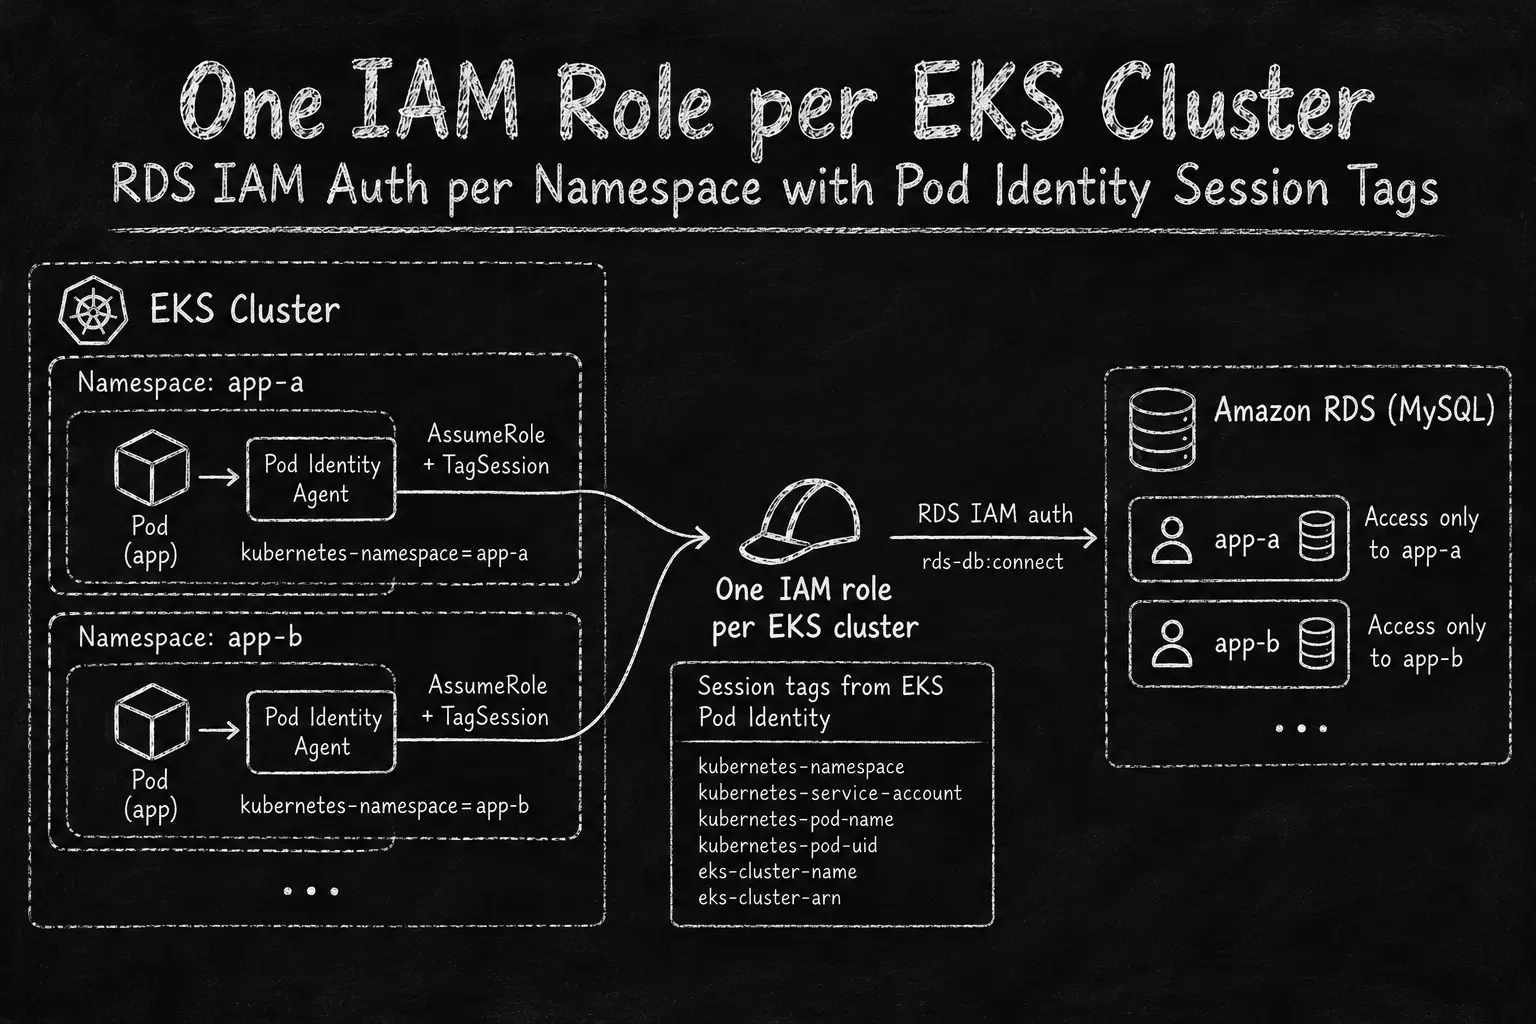
EKS namespaces mapped to matching RDS database users through one shared IAM role

One IAM Role per EKS Cluster: RDS IAM Auth per Namespace with Pod Identity Session Tags

If you are running the same application for many tenants in Kubernetes, most likely you deploy a separate copy of it for each tenant, in its own namespace. In this post I call each copy an app. All apps run the same code and need the same access. The only difference is the name: the database user, the S3 prefix, the parameter path and so on. Every app needs its own RDS user and password. It is fine when you have up to 10 apps. If you have more, you need a procedure to rotate the passwords, and managing all of that is overcomplicated. ...

October 21, 2026 · 10 min · 1987 words · Serhii Kaidalov
External Secrets Operator reading AWS Secrets Manager through EKS Pod Identity

External Secrets Operator with ABAC for AWS Secrets Manager using EKS Pod Identity

There is a great article on the AWS Blog: How to use AWS Secrets Manager and ABAC for enhanced secrets management in Amazon EKS . The only downside of that approach is that it uses OpenID Connect (OIDC) and IRSA for authentication. But there is now a better and simpler option: Amazon EKS Pod Identity . ...

December 1, 2025 · Last Modified: October 21, 2026 · 6 min · 1121 words · Serhii Kaidalov