Donate to support Ukraine's independence.
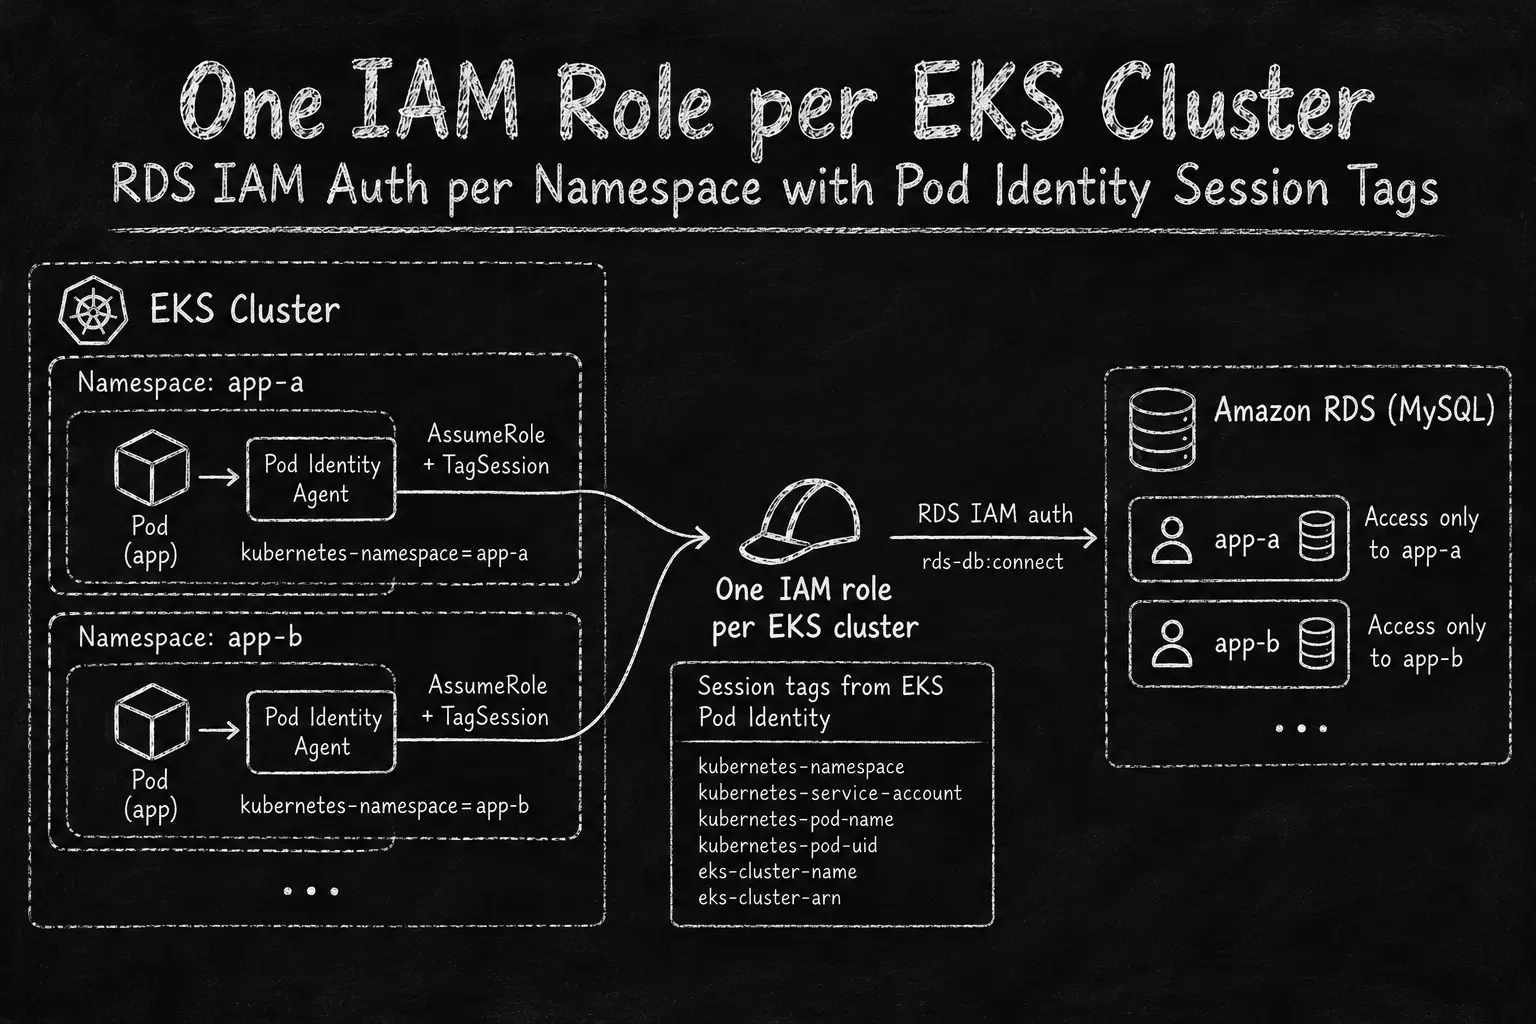
EKS namespaces mapped to matching RDS database users through one shared IAM role

One IAM Role per EKS Cluster: RDS IAM Auth per Namespace with Pod Identity Session Tags

If you are running the same application for many tenants in Kubernetes, most likely you deploy a separate copy of it for each tenant, in its own namespace. In this post I call each copy an app. All apps run the same code and need the same access. The only difference is the name: the database user, the S3 prefix, the parameter path and so on. Every app needs its own RDS user and password. It is fine when you have up to 10 apps. If you have more, you need a procedure to rotate the passwords, and managing all of that is overcomplicated. ...
October 21, 2026 · 10 min · 1987 words · Serhii Kaidalov
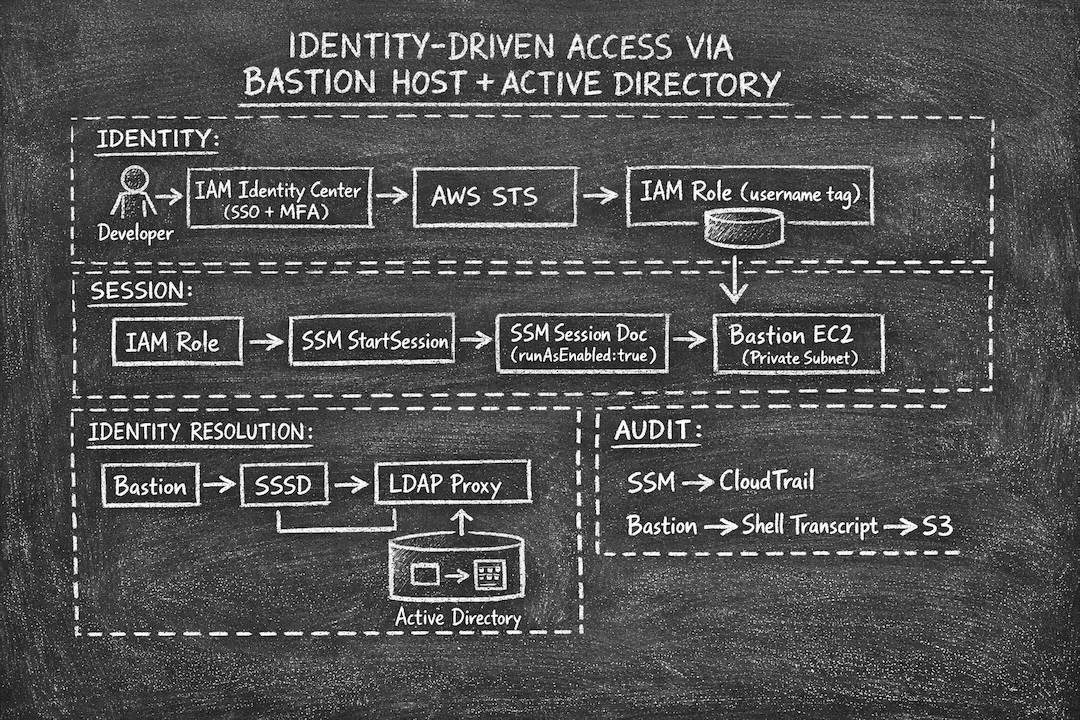
An SSM bastion host authenticating users through Active Directory

Identity-Driven Access to Internal Resources Using AWS SSM. Part 2: Bastion Host with Active Directory

Identity-Driven Access via Bastion Host and Active Directory Note Part 1 covers SSM port forwarding as a zero-trust replacement for VPN - identity-driven access to internal AWS resources without VPN or SSH keys. ...

March 29, 2026 · Last Modified: September 29, 2026 · 11 min · 2315 words · Serhii Kaidalov
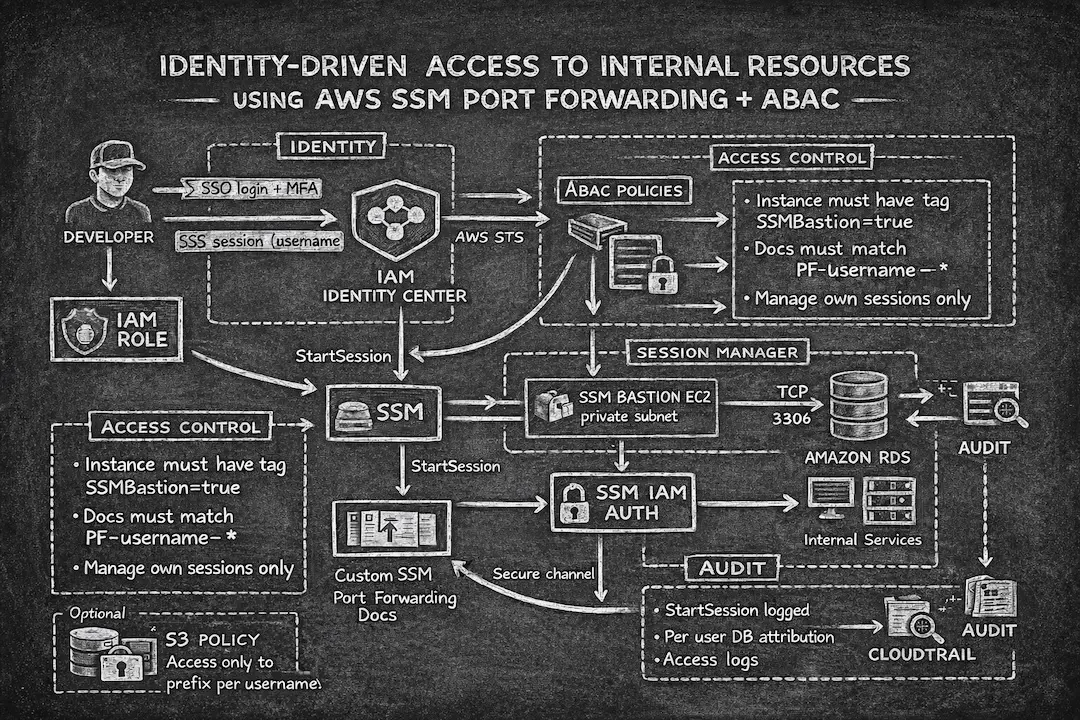
Zero-trust SSM port forwarding controlled by identity-based access rules

Identity-Driven Access to Internal Resources Using AWS SSM. Part 1: Zero-Trust Port Forwarding

Identity-Driven Access to Internal Resources Using AWS SSM Port Forwarding and ABAC Traditional access to private AWS infrastructure usually relies on VPN connectivity and direct subnet reachability. It works, but it also increases attack surface, enables lateral movement, and makes auditing harder. This article describes a different approach: An identity-driven, zero-trust access model built on: AWS IAM Identity Center (SSO + MFA) (Optional) AWS Systems Manager Session Manager port forwarding Attribute-Based Access Control (ABAC) No direct subnet access. No shared passwords. No SSH key distribution. ...

February 26, 2026 · Last Modified: September 29, 2026 · 9 min · 1715 words · Serhii Kaidalov
External Secrets Operator reading AWS Secrets Manager through EKS Pod Identity

External Secrets Operator with ABAC for AWS Secrets Manager using EKS Pod Identity

There is a great article on the AWS Blog: How to use AWS Secrets Manager and ABAC for enhanced secrets management in Amazon EKS . The only downside of that approach is that it uses OpenID Connect (OIDC) and IRSA for authentication. But there is now a better and simpler option: Amazon EKS Pod Identity . ...

December 1, 2025 · Last Modified: October 21, 2026 · 6 min · 1121 words · Serhii Kaidalov
Fail2ban reading Nginx logs and banning attackers in Cloudflare

Auto-Ban Attackers in Cloudflare Using Fail2ban and Nginx Logs

Many of us use CloudFlare to protect our websites and services from malicious activity. In this post, I’ll show you how to configure Fail2ban to block bad actors directly on CloudFlare. Nginx setup Before we start, make sure your Nginx logs contain real client IP addresses. If your logs still show CloudFlare IPs, follow my earlier guide: Handling Real IP in Nginx Behind Load Balancer and Cloudflare ...

November 22, 2025 · Last Modified: October 21, 2026 · 3 min · 547 words · Serhii Kaidalov
A YubiKey securing SSH authentication and signed git commits on macOS

Harden SSH and Git Commits with a Hardware Key (YubiKey) on macOS

What is a YubiKey? A YubiKey is a small hardware device used as a second factor of authentication. It works similarly to one-time codes sent by SMS or email - but much more securely. To authenticate, the YubiKey must be physically inserted into your computer or connected via NFC. This makes it nearly impossible for remote attackers to compromise your credentials. Getting a YubiKey The best place to buy a YubiKey is directly from Yubico . You can also buy them from trusted retailers, but always verify the device is genuine using Yubico’s verification page . ...

November 6, 2025 · Last Modified: October 21, 2026 · 5 min · 939 words · Serhii Kaidalov
cert-manager and trust-manager distributing a CA bundle between Kubernetes services

Fix TLS Trust Errors Between Kubernetes Services with cert-manager and trust-manager

Managing Internal TLS Trust in Kubernetes with cert-manager and trust-manager How do you maintain a secure SSL/TLS connection between services within a Kubernetes cluster? One simple (but unsafe) answer is to create a self-signed certificate and skip verification with a flag like --insecure-skip-tls-verify. A more advanced solution is to use a service mesh (e.g., Linkerd, Istio), which automatically manages certificates and trust. But what if you want something simpler and lighter? That’s where trust-manager comes in. It’s the easiest way to manage trust bundles in Kubernetes and OpenShift clusters. ...

October 27, 2025 · Last Modified: October 21, 2026 · 5 min · 853 words · Serhii Kaidalov
An SSH login on a server triggering a Telegram alert

Get a Telegram Alert Every Time Someone Logs Into Your Server

SSH Telegram Notify Have you ever wanted to get a Telegram notification when someone logs into your server via SSH? I did! I also wanted to automate the entire setup with Ansible for faster deployment and updates. So, I created an Ansible role that does exactly that. It automatically configures your servers to send login/logout notifications to Telegram. It currently supports Debian/Ubuntu, but can easily be extended to other Linux distributions. ...

October 10, 2025 · Last Modified: September 29, 2026 · 3 min · 596 words · Serhii Kaidalov
CloudTrail events triggering infrastructure change notifications

CloudTrail: Infrastructure changes notifications

AWS infrastructure changes notifications with Slack CloudTrail is a powerful service that helps audit the actions of users and roles in your AWS account. It can be integrated with other services to improve the way you react to infrastructure changes. This is especially useful for large projects. In this article, we’ll describe both a basic and an improved way to track infrastructure changes in your AWS account and send notifications to Slack. ...

October 5, 2025 · Last Modified: September 29, 2026 · 5 min · 968 words · Mykhailo Babych
AWS SSM port forwarding to a private resource without open inbound ports

Access Private AWS Resources Without Opening Firewall Ports Using SSM

Do you want a secure and convenient way to access internal AWS resources - like RDS databases or EC2 instances - from your local machine? Me too! Thanks to AWS Systems Manager (SSM), you can get shell access to EC2 instances without opening any inbound ports. Even better, since 2022, AWS also supports port forwarding over SSM, allowing access to nearly any internal AWS resource from your laptop - without requiring a bastion host with internet access. ...

April 21, 2025 · Last Modified: September 29, 2026 · 2 min · 422 words · Serhii Kaidalov