Donate to support Ukraine's independence.
Generated by AI

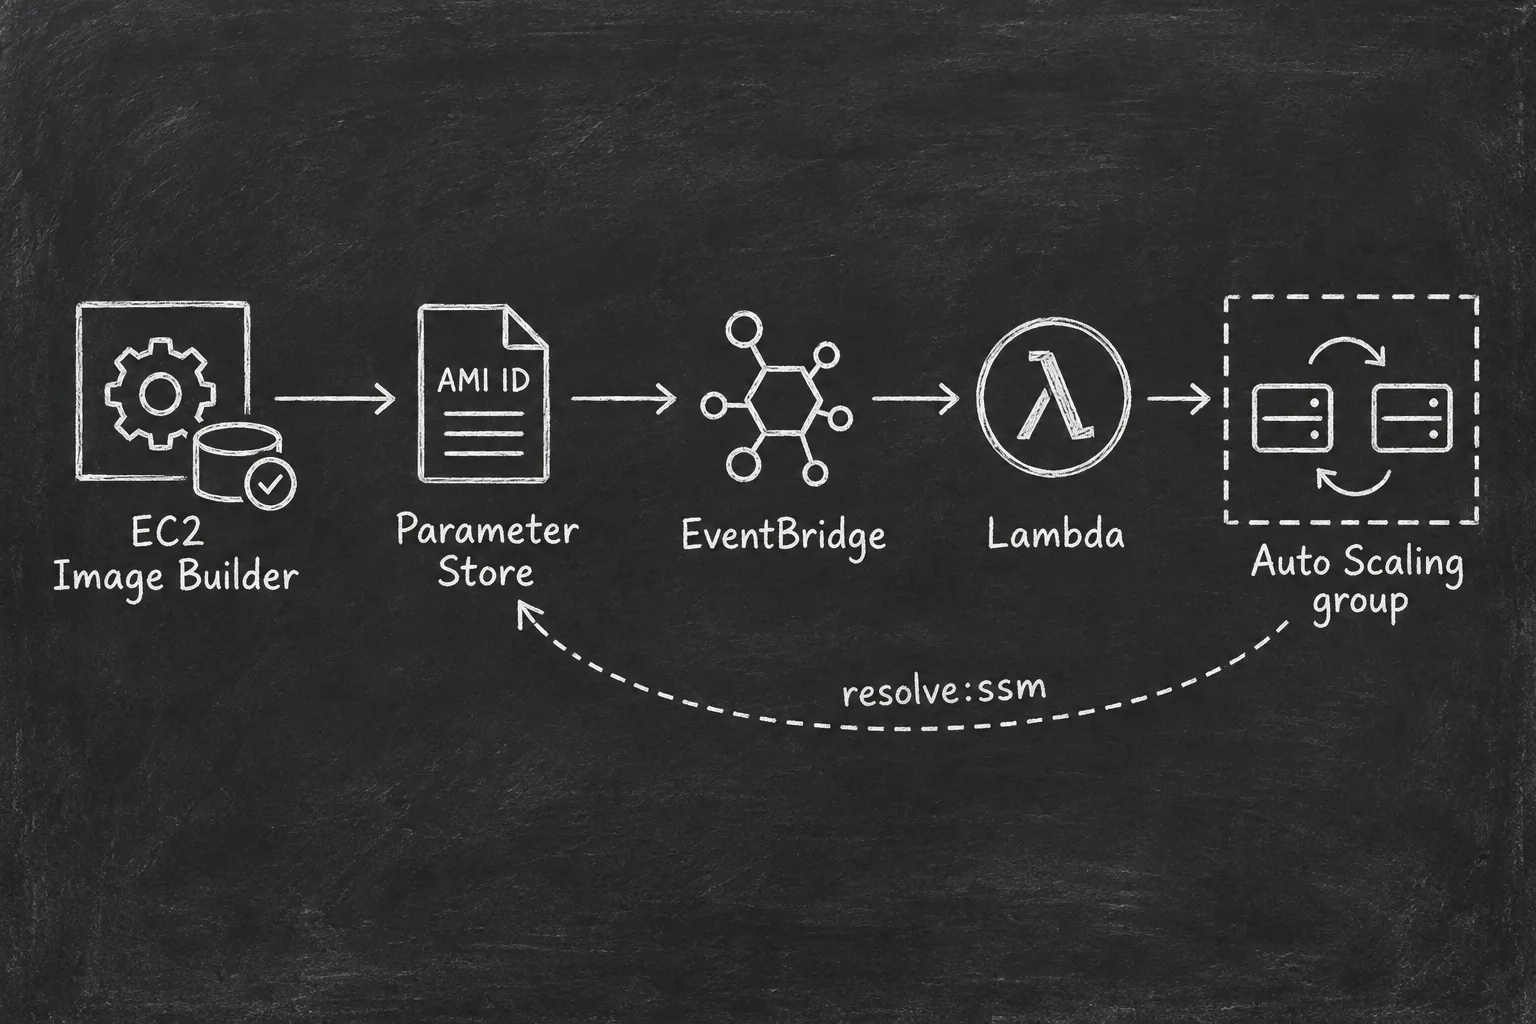
AMI rollouts with EC2 Image Builder and Parameter Store

Building a new AMI is only part of updating EC2 instances. We still need to tell the Auto Scaling group to use it and replace the instances running the old image. EC2 Image Builder can write the output AMI ID to a parameter during distribution. A launch template can reference that parameter directly. The remaining part is to start an instance refresh when the value changes, which is not something natively supported by AWS. ...
September 14, 2026 · 9 min · 1819 words · Serhii Kaidalov
Generated by AI

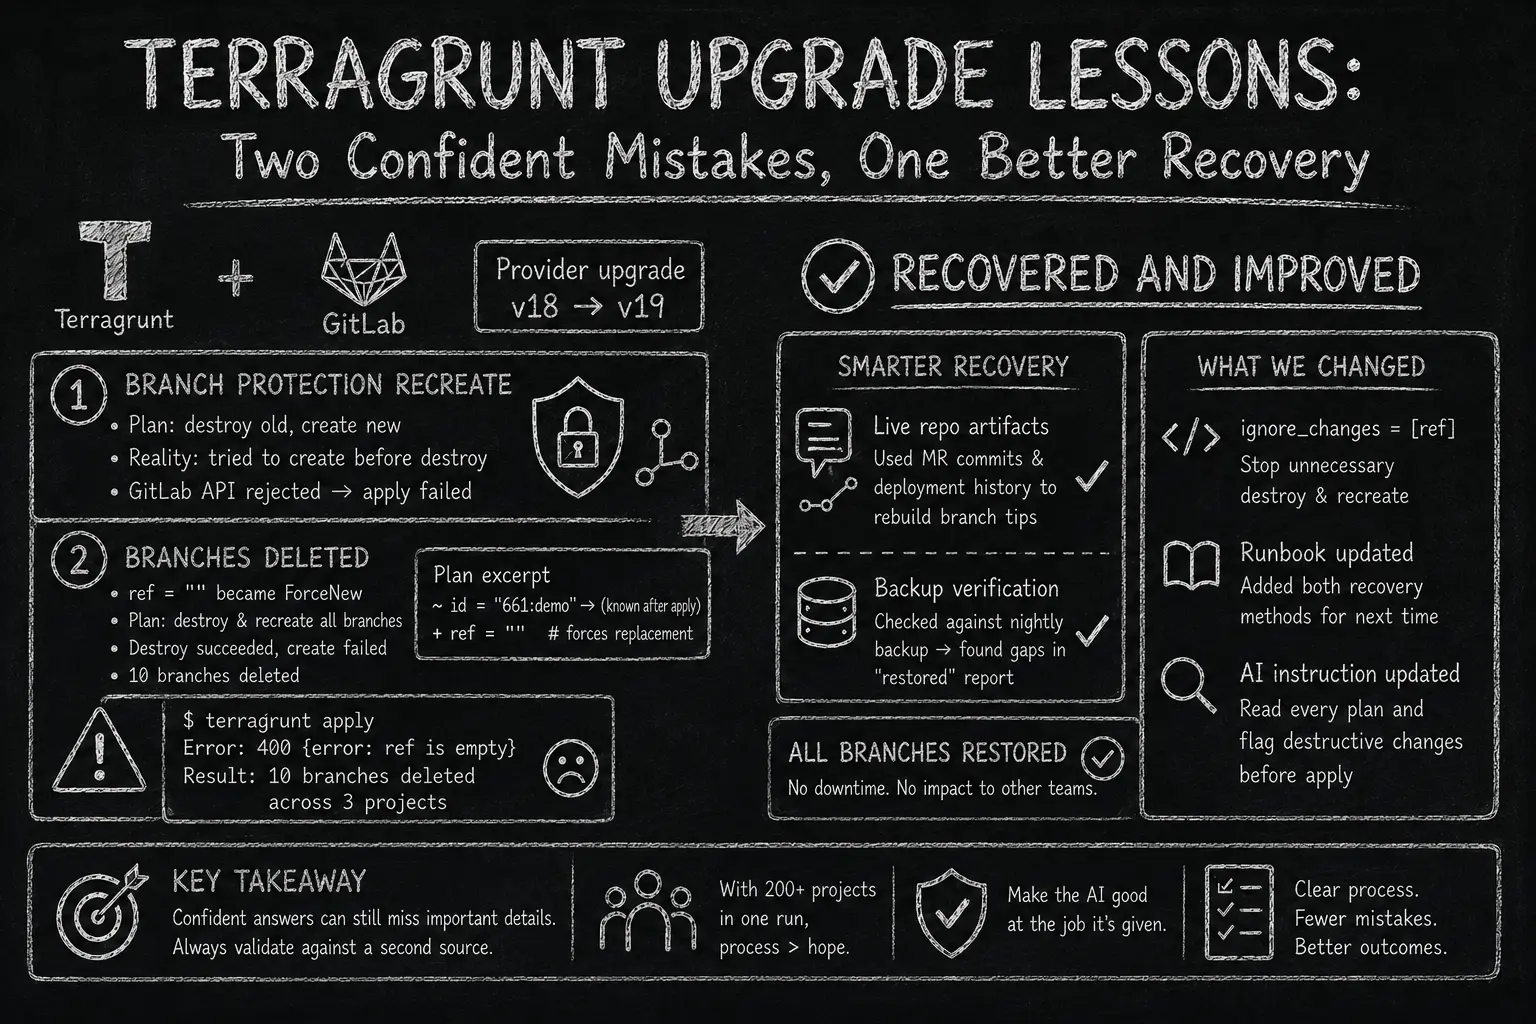
GitLab, Terraform, and Two AI Mistakes in One Afternoon

We manage a self-hosted GitLab instance entirely through Terraform: groups, projects, branch protection, and even git branches. All of it lives in one shared module and gets applied with Terragrunt. We upgraded that module’s provider from v18 to v19. The whole thing took about two or three hours. In that time, an AI assistant sounded confident twice about things that were not fully correct. I caught only one of the two mistakes in time, and only because checking a confident answer against something else was already a habit for me, not because I noticed a problem first. ...

July 8, 2026 · 7 min · 1365 words · Serhii Kaidalov
Generated by AI

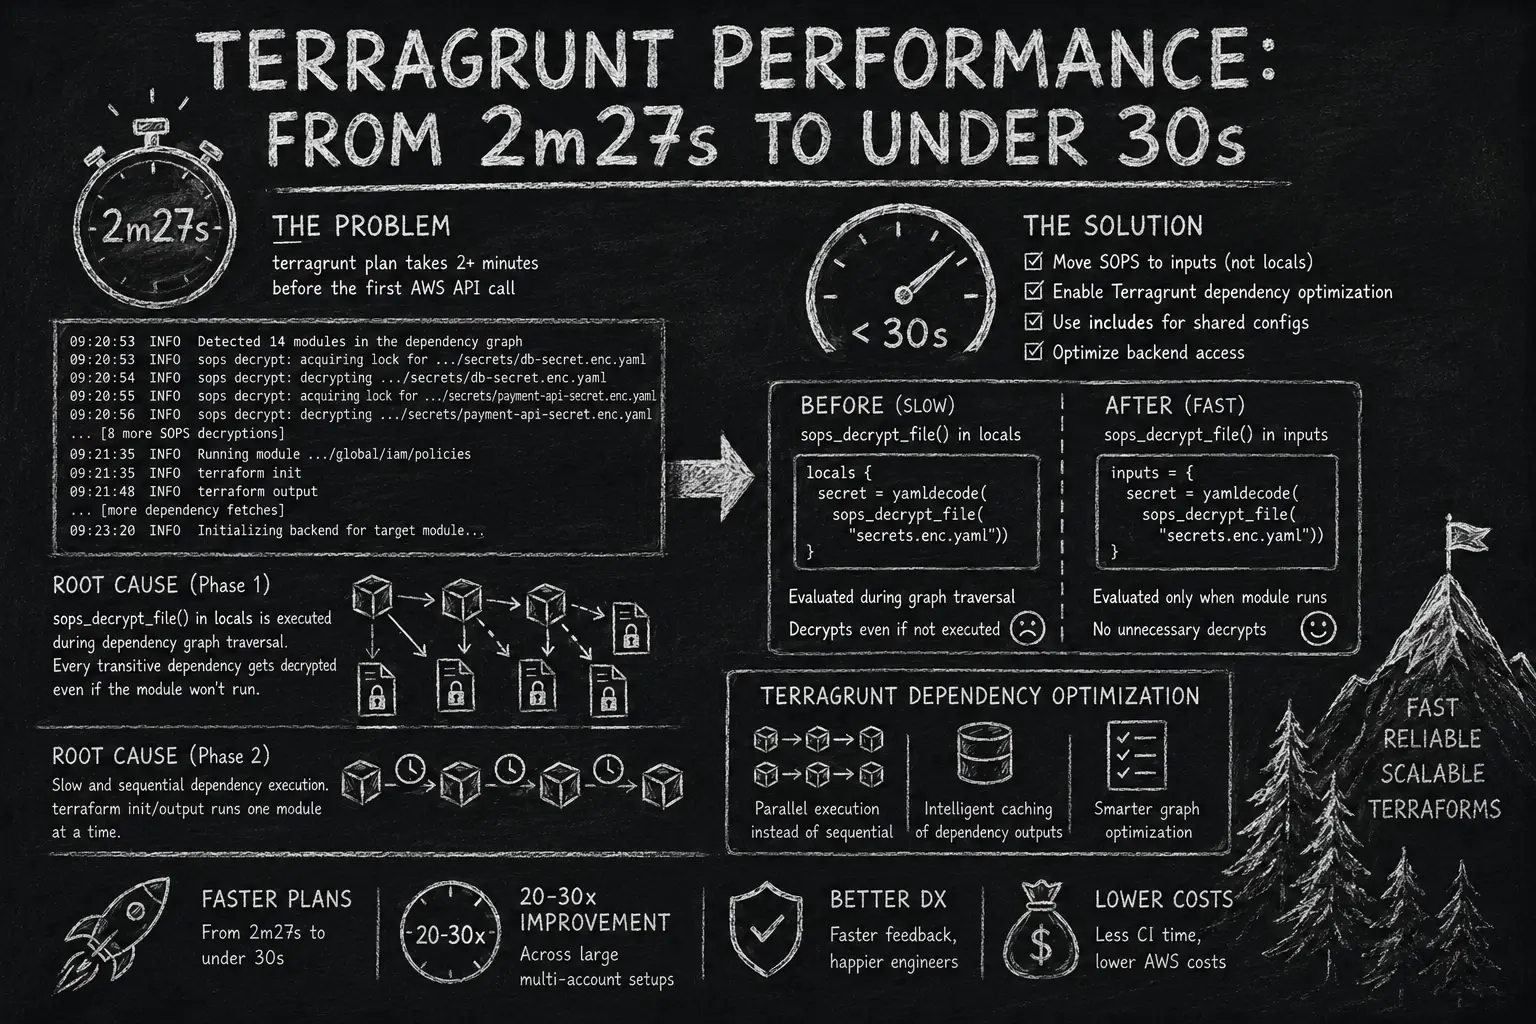
Terragrunt Performance: From 2m27s to Under 30s

When terragrunt plan on a single module takes over two minutes before showing a single AWS API call, something is wrong. This post covers two distinct performance problems I found and fixed in a large multi-account Terragrunt setup (~15 AWS accounts, 400+ modules). The Problem Running terragrunt plan on our EKS cluster module was taking 2 minutes 27 seconds just to start. With debug logging enabled, the culprit was clear: ...

June 26, 2026 · 6 min · 1081 words · Serhii Kaidalov
Generated by AI

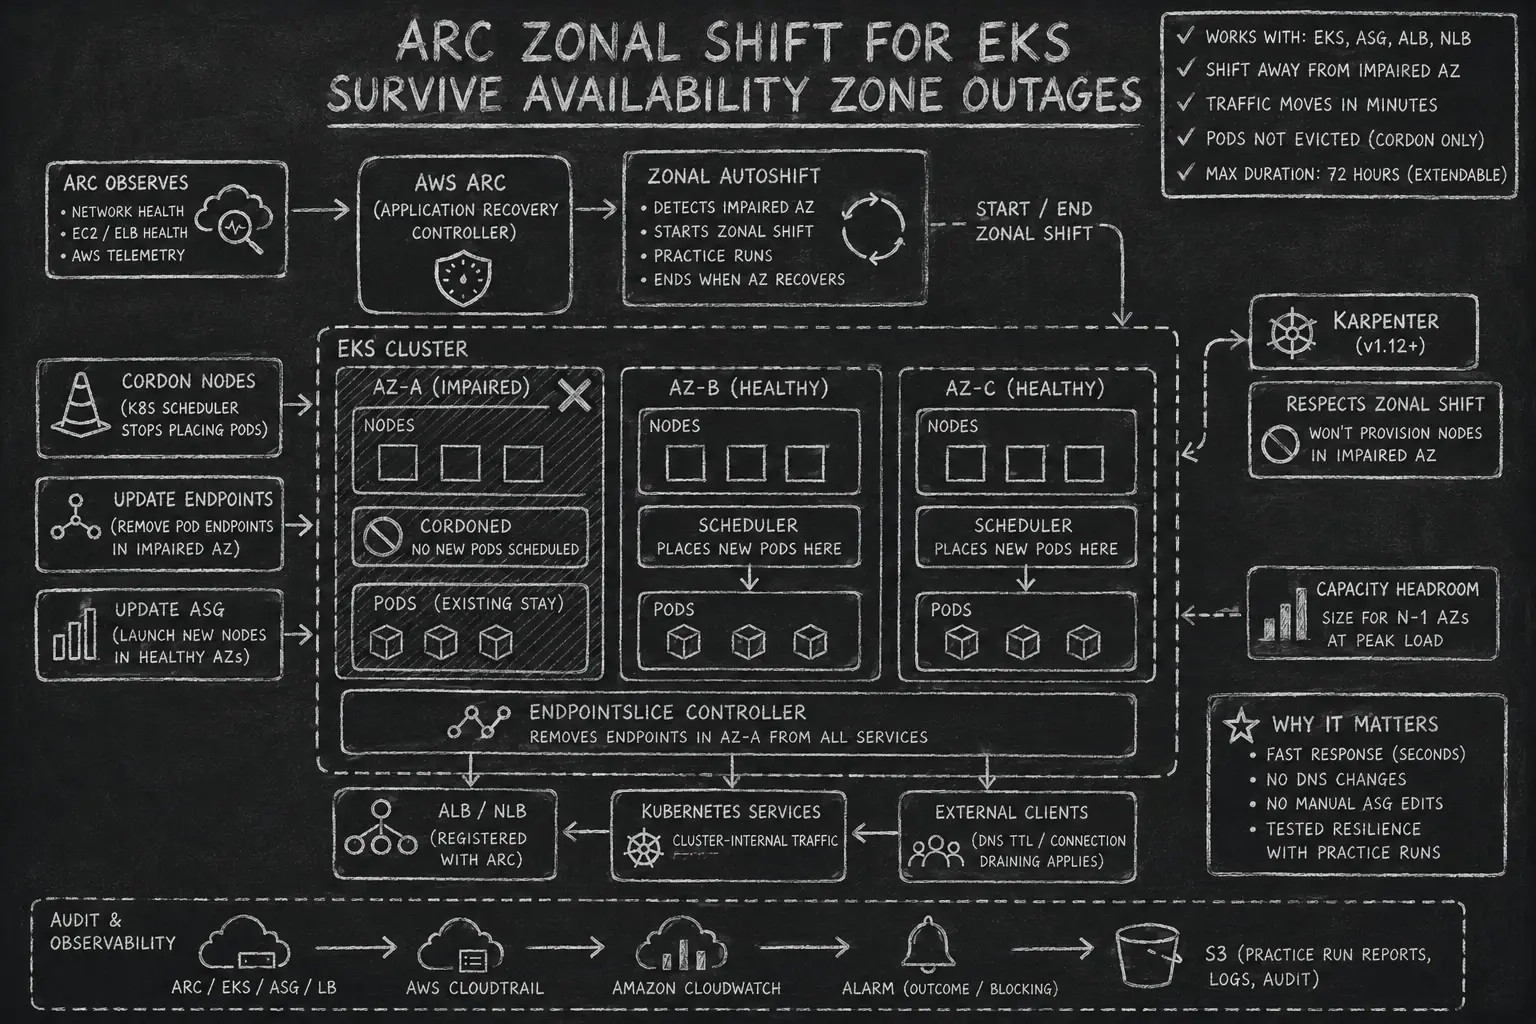
ARC Zonal Shift for EKS: Survive Availability Zone Outages

Earlier this year, AWS had a major Availability Zone outage in us-east-1. Only one AZ went down, but if your workloads were running there, you know how it went: alerts firing, runbooks open, manual fixes, and a race to move traffic before customers noticed. For those who were not lucky enough to be in a different AZ, it raised an obvious question: why isn’t there a button for this? There is. It’s called ARC Zonal Shift. ...

June 19, 2026 · 8 min · 1670 words · Serhii Kaidalov
Generated by AI

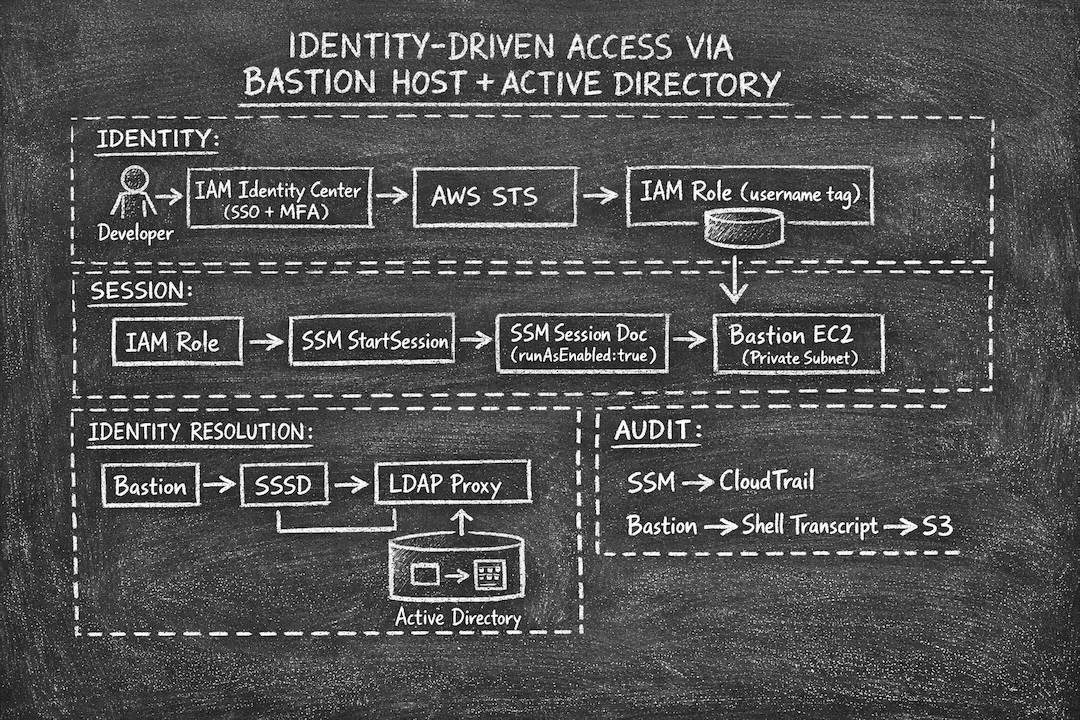
Identity-Driven Access to Internal Resources Using AWS SSM. Part 2: Bastion Host with Active Directory

Identity-Driven Access via Bastion Host and Active Directory Note Part 1 covers SSM port forwarding as a zero-trust replacement for VPN - identity-driven access to internal AWS resources without VPN or SSH keys. ...

March 29, 2026 · 11 min · 2315 words · Serhii Kaidalov
Generated by AI

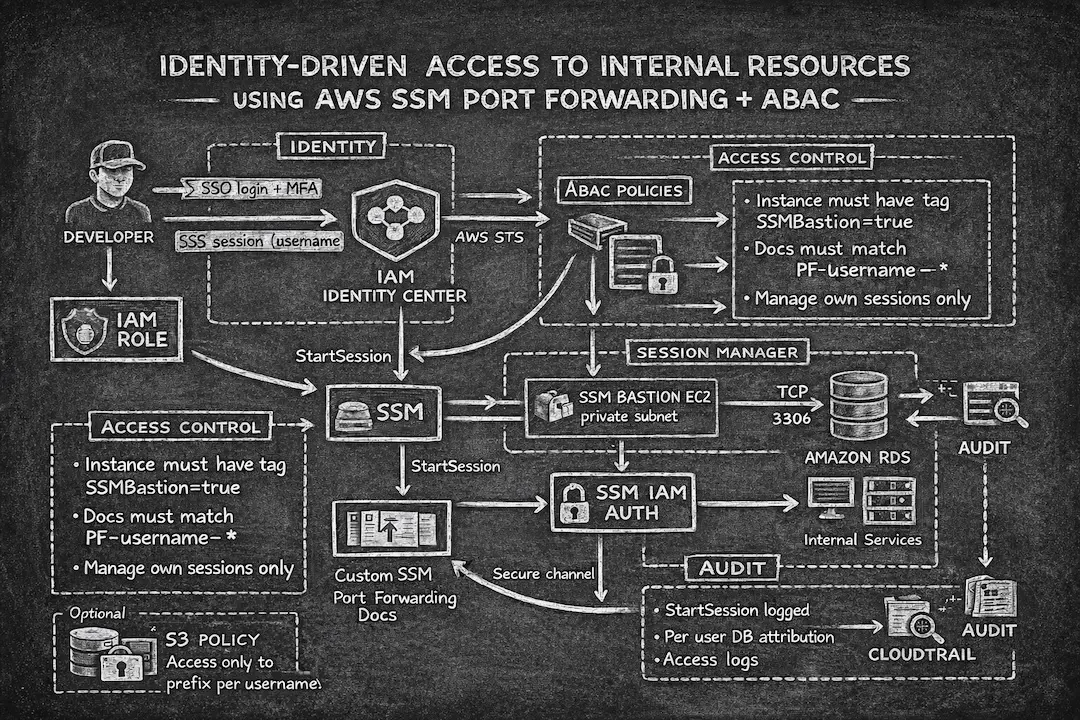
Identity-Driven Access to Internal Resources Using AWS SSM. Part 1: Zero-Trust Port Forwarding

Identity-Driven Access to Internal Resources Using AWS SSM Port Forwarding and ABAC Traditional access to private AWS infrastructure usually relies on VPN connectivity and direct subnet reachability. It works, but it also increases attack surface, enables lateral movement, and makes auditing harder. This article describes a different approach: An identity-driven, zero-trust access model built on: AWS IAM Identity Center (SSO + MFA) (Optional) AWS Systems Manager Session Manager port forwarding Attribute-Based Access Control (ABAC) No direct subnet access. No shared passwords. No SSH key distribution. ...

February 26, 2026 · 9 min · 1715 words · Serhii Kaidalov
Generated by AI

How to Migrate kube-proxy from IPVS to nftables Without Breaking Your Cluster

Switching kube-proxy mode from IPVS to nftables Many of you have heard about the nginx-ingress controller retirement, right? But have you also heard about the deprecation of IPVS mode in Kubernetes 1.35? Kubernetes 1.35 release notes: https://kubernetes.io/blog/2025/12/17/kubernetes-v1-35-release/#deprecation-of-ipvs-mode-in-kube-proxy If your Kubernetes clusters are running kube-proxy in IPVS mode, it is time to prepare for switching to nftables. What I found interesting is that the official AWS EKS documentation still recommends IPVS mode, with only a small mention that nftables is ‘in development’: https://docs.aws.amazon.com/eks/latest/best-practices/ipvs.html ...

January 10, 2026 · 2 min · 372 words · Serhii Kaidalov
Generated by AI

External Secrets Operator with ABAC for AWS Secrets Manager using EKS Pod Identity

There is a great article on the AWS Blog: How to use AWS Secrets Manager and ABAC for enhanced secrets management in Amazon EKS . The only downside of that approach is that it uses OpenID Connect (OIDC) and IRSA for authentication. But there is now a better and simpler option: Amazon EKS Pod Identity . ...

December 1, 2025 · 6 min · 1121 words · Serhii Kaidalov
Generated by AI

Auto-Ban Attackers in Cloudflare Using Fail2ban and Nginx Logs

Many of us use CloudFlare to protect our websites and services from malicious activity. In this post, I’ll show you how to configure Fail2ban to block bad actors directly on CloudFlare. Nginx setup Before we start, make sure your Nginx logs contain real client IP addresses. If your logs still show CloudFlare IPs, follow my earlier guide: Handling Real IP in Nginx Behind Load Balancer and Cloudflare ...

November 22, 2025 · 3 min · 547 words · Serhii Kaidalov
Generated by AI

Harden SSH and Git Commits with a Hardware Key (YubiKey) on macOS

What is a YubiKey? A YubiKey is a small hardware device used as a second factor of authentication. It works similarly to one-time codes sent by SMS or email - but much more securely. To authenticate, the YubiKey must be physically inserted into your computer or connected via NFC. This makes it nearly impossible for remote attackers to compromise your credentials. Getting a YubiKey The best place to buy a YubiKey is directly from Yubico . You can also buy them from trusted retailers, but always verify the device is genuine using Yubico’s verification page . ...

November 6, 2025 · 5 min · 939 words · Serhii Kaidalov